What Apple's '@apple.com #123456' verification code manner
 [ad_1]
In case you have logged in just lately together with your Apple ID and requested an SMS-based second-factor verification code as an alternative of the usage of the relied on software means, you may have spotted Apple made a metamorphosis to the textual content you obtain.
In the past, Apple despatched a message like this:
Your Apple ID Code is 123456. Don’t percentage it with someone.
Beginning round November 2021, the codes seem on this structure:
Your Apple ID Code is: 123456. Don’t percentage it with someone. @apple.com #123456 %apple.com
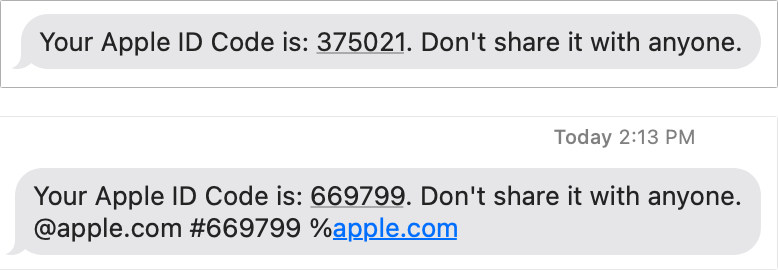
Why the trade? Apple proposed in August 2020 that it could give a boost to “domain-bound codes” for logins. This type of code calls for websites make a slight addition to the textual content messages used for verification codes. The incoming message has to offer a vacation spot area and a few different information. Apple mentioned that this alteration would support the integrity of its running methods providing to autofill the code by the use of an offer within the QuickType bar in iOS and iPadOS and a drop-down price in macOS Safari and different macOS apps that benefit from this selection.
Apple proposed this alteration to be able to deter phishing that tries to intercept and redirect verification codes. In maximum phishing assaults, the sufferer will get directed to a faux web site that asks them to go into their credentials. The web site takes the ones credentials and silently relays them to login on the reliable web site.
However some attackers are sensible to two-factor authentication. If the web site sends a code by the use of SMS because the default means, the person being phished receives a textual content message with the code. The phisher then activates for that code.
iOS, iPadOS, and macOS be offering to fill within the code maximum just lately arrived by the use of SMS to the Messages app in any correctly formatted box—together with a phishing web site’s verification-code box. That makes it too simple at the scammers.
Then again, if the textual content message is scoped as Apple recommended, running methods beginning with iOS 15, iPadOS 15, and macOS 11 Large Sur will most effective be offering to autofill on websites that fit the area identify. The safety isn’t easiest, however it’s a easy replace to improve defensive movements.
The structure in most cases looks as if this:
- A normal human-readable message, together with the code, adopted by way of a brand new line.
- The scoped area as
@area.tld. - The code repeated once more as
#123456. - If the web site makes use of an embedded HTML component, known as an iframe, the supply of the iframe is indexed after %, reminiscent of
%ecommerce.instance. (The unique spec specifies @; Apple seems to be the usage of % for its texts.)
As a person, there’s not anything you wish to have to do. The SMS codes proceed to autofill as anticipated for legitimate websites.
Then again, you'll workout higher vigilance: while you obtain a code on this structure as a textual content message and your app or browser doesn’t be offering to autofill it, that you must be topic to a phishing lure. Examine the area or app moderately ahead of continuing.
This Mac 911 article is in line with a query submitted by way of Macworld reader Kevin.
Ask Mac 911
We’ve compiled an inventory of the questions we get requested maximum ceaselessly, together with solutions and hyperlinks to columns: read our super FAQ to peer in case your query is roofed. If no longer, we’re at all times on the lookout for new issues to unravel! E-mail yours to mac911@macworld.com, together with display captures as suitable and whether or not you wish to have your complete identify used. No longer each query shall be replied, we don’t respond to electronic mail, and we can not supply direct troubleshooting recommendation.


Comments
Post a Comment