5 HTTP Safety Headers You Want To Know For Search engine marketing-Search engine marketing Guide
 [ad_1]
Safety headers are simply overpassed in website online audits.
Whilst some would possibly say that website online safety isn't an Search engine marketing-related worry, it does grow to be Search engine marketing-related when a web page turns into hacked and seek visitors dwindles to 0.
Safety headers will have to be a best worry of everybody who publishes anything else at the Web.
The excellent news is that they're moderately easy to configure and can lend a hand stay your website online and its guests secure.
on this column, you’ll be told what safety headers are and the way they paintings in addition to the highest 5 safety headers, put in force them, which WordPress plugins you'll use for environment safety headers, and extra.
Let’s get began!
What Are Safety Headers?
Safety headers are directives browsers will have to apply which are handed alongside during the HTTP header reaction.
An HTTP header is a reaction by means of a internet server to a browser that is making an attempt to get entry to a internet web page.
The header reaction communicates issues corresponding to when the internet web page does now not exist (400 reaction header).
Or that it’s alright to obtain a font from Google however to not agree with another information out of doors of the website online’s area.
In that instance, the section that tells the browser that it’s alright to obtain Google fonts however now not agree with any information originating somewhere else as opposed to the website online itself is a safety directive.
A safety directive like that can block a browser from downloading malicious information from any other website online.
Safety headers introduce restrictions and directions that save you accidental safety occasions.
Why Use Safety Headers?
Computerized bot device are continuously probing and trying out web pages for safety weaknesses.
Those vulnerabilities can also be offered by means of the content material control gadget, by means of the JavaScript library used so as to add capability, and for safety weaknesses offered by means of a plugin or a theme.
Web pages that use safety headers are mentioned to be hardened in opposition to safety threats.
Whilst a website online can get alongside with out the use of safety headers by means of maintaining its parts up to the moment and the use of safety plugins, doing so needlessly exposes the website online and the web page guests to safety dangers.
As an example, safety plugins can’t prevent advert injections that rob a web page proprietor of advert income.
Most likely the most productive explanation why to make use of safety headers is as a result of they're moderately simple to put in force and be sure that a website online assists in keeping working most often.
Most sensible 5 Safety Headers
1. Content material-Safety-Coverage (CSP)
A content material safety coverage (CSP) is helping to give protection to a website online and the web page guests from Move Website online Scripting (XSS) assaults and from information injection assaults.
Move-Website online Scripting (XSS)
Move-Website online Scripting (XSS) exploits occur when hackers benefit from a safety hollow to add malicious scripts to a website online which can be then downloaded to a sufferer’s browser.
XSS assaults benefit from flaws in a content material control gadget that permits sudden inputs to be injected as a result of inadequate consumer enter document sanitization.
As an example, ordinarily, an e-mail shape will have to be coded to be expecting a limited enter.
A poorly coded shape would possibly permit another enter which will then result in an injection of malicious information.
An XSS assault can be utilized to scouse borrow passwords or as a part of a multi-step hacking tournament.
Injection Assaults
The Open Internet Utility Safety Mission (OWASP) describes injection assaults as a significant safety possibility:
“Injection is an attacker’s try to ship information to an utility in some way that can exchange the which means of instructions being despatched to an interpreter.
As an example, the commonest instance is SQL injection, the place an attacker sends “101 OR 1=1” as an alternative of simply “101”. When incorporated in a SQL question, this information adjustments the which means to go back ALL information as an alternative of only one.
…Incessantly those interpreters run with numerous get entry to, so a a hit assault can simply lead to vital information breaches, and even lack of keep an eye on of a browser, utility, or server. Taken in combination, injection assaults are an enormous proportion of the intense utility safety possibility.”
The content material safety coverage on its own does now not 100% offer protection to a web page from assaults however it does lend a hand to decrease the potential for a move web page scripting assault.
A CSP header instructs the browser to just obtain sources from a suite team of domain names and handiest from the ones domain names.
Any attacker this is downloading malicious scripts from any other server out of doors of that depended on team might be blocked.
Making a content material safety coverage can also be as strict or as lenient as a writer calls for.
Caution: Then again, environment one up could be a little tough as a result of you need to listing the entire scripts and sources which are being downloaded from out of doors of your area so as to whitelist them.
2. Strict-Delivery-Safety Header (HSTS)
The Strict-Delivery-Safety Header is also known as the HTTP Strict Delivery Safety header (HSTS).
Many web pages handiest have a 301 redirect from HTTP to HTTPS.
However that’s now not sufficient to stay the website online safe since the website online remains to be prone to a man-in-the-middle assault.
HSTS prevents an attacker from downgrading the HTTPS connection to an HTTP connection which then lets in the attacker to benefit from insecure redirects.
As an example, if an individual sorts in instance.com to get entry to a web page, with out in fact typing within the https section (or they only sort http out of dependancy), then the chance exists for a man-in-the-middle assault.
That more or less assault can compromise the web page guests’ connection to the website online and any delicate data exchanged between the customer and the website online turns into visual to the attacker.
As an example, an attacker can intercept cookies that comprise delicate data like login credentials.
The US executive lists 3 eventualities the place HTTPS can also be downgraded to HTTP and therefore permit an attacker to compromise safety.
Those are the 3 ways HTTPS can also be downgraded:
- When a consumer sorts “gsa.gov” into the URL bar, browsers default to the use of http://.
- A consumer would possibly click on on an outdated hyperlink that mistakenly makes use of an http:// URL.
- A consumer’s community could also be antagonistic and actively rewrite https:// hyperlinks to http://.
The HSTS header prevents this from going down by means of forcing the browser to completely now not settle for an HTTP connection.
The HTTP Strict Delivery Safety (HSTS) header tells the browser that all of the website online will have to handiest be accessed by means of a safe HTTPS protocol.
Facet Observe: How To Preload HSTS Into Chrome
On a connected notice, Google Chrome has an HSTS Preload program the place publishers can publish their websites to be indexed by means of Chrome as handiest obtainable by means of the HTTPS protocol.
Many Chrome-based internet browsers will therefore preload those web pages with HTTPS and handiest by means of HTTPS, exhausting coding that normal proper into the browser.
Qualifying websites will have to already be serving the HSTS safety header.
Those are the 4 necessities had to qualify for Chrome HSTS preloading:
- “Serve a legitimate certificates.
- Redirect from HTTP to HTTPS at the similar host, in case you are listening on port 80.
- Serve all subdomains over HTTPS. Specifically, you will have to give a boost to HTTPS for the www subdomain if a DNS document for that subdomain exists.
- Serve an HSTS header at the base area for HTTPS requests:- The max-age will have to be a minimum of 31536000 seconds (1 yr).- The includeSubDomains directive will have to be specified.- The preload directive will have to be specified.- If you're serving an extra redirect out of your HTTPS web page, that redirect will have to nonetheless have the HSTS header (slightly than the web page it redirects to).
You’ll in finding additional info at hstspreload.org.
3. X-Content material-Sort-Choices
This safety header stops sure sorts of exploits that may occur, for instance, via malicious user-generated content material.
Browsers can “sniff” if a content material is a picture (.jpg), a film (.mp4), or textual content, HTML, JavaScript, and different sorts of content material that may be downloaded from a website online.
The “sniffing” lets in a browser to obtain the internet web page parts and accurately render them, specifically in eventualities when the metadata the browser must render the component is lacking.
Sniffing lets in the browser to determine what the component is (a picture, textual content, and so forth.) after which render that component.
Hackers then again will attempt to trick browsers into considering that a destructive JavaScript document is in fact a picture, permitting the browser to obtain the document after which therefore executing that document, inflicting any collection of unfavorable results for that web page customer, particularly with what’s referred to as a Power-by Obtain Assault.
The X-Content material-Sort-Choices header can prevent that and different connected assaults by means of disabling the facility of browsers from “sniffing” for the content material sort.
4. X-Body-Choices
The X-Body-Choices safety header is helping prevent click-jacking assaults.
Mozilla describes Click on-jacking as:
“…the follow of tricking a consumer into clicking on a hyperlink, button, and so forth. this is as opposed to what the consumer thinks it's.
This can be utilized, for instance, to scouse borrow login credentials or to get the consumer’s unwitting permission to put in a work of malware.”
The X-Body-Choices header works by means of combating a internet web page from being rendered inside of an iframe, for instance.
It prevents extra than simply iframe-based assaults, despite the fact that.
Microsoft defines body sniffing on this means:
“Framesniffing is an assault method that takes good thing about browser capability to scouse borrow information from a website online.
Internet packages that permit their content material to be hosted in a cross-domain IFRAME could also be prone to this assault.
The X-Body-Choices header can be utilized to keep an eye on whether or not a web page can also be positioned in an IFRAME.
For the reason that Framesniffing method is determined by with the ability to position the sufferer web page in an IFRAME, a internet utility can offer protection to itself by means of sending an acceptable X-Body-Choices header.”
The Open Internet Utility Safety Mission (OWASP) supplies a useful rationalization of click-jacking assaults:
“…consider an attacker who builds a internet web page that has a button on it that claims “click on right here for a loose iPod”.
Then again, on best of that internet web page, the attacker has loaded an iframe together with your mail account, and coated up precisely the “delete all messages” button immediately on best of the “loose iPod” button.
The sufferer tries to click on at the “loose iPod” button however as an alternative in fact clicked at the invisible “delete all messages” button.
In essence, the attacker has “hijacked” the consumer’s click on, therefore the identify “Clickjacking”.”
The X-Body-Choices header is vital for shielding your web page guests in addition to your web page’s popularity.
The OWASP internet web page on click-jacking is going on to explain how Adobe Flash fell sufferer to a click-jacking assault that allowed hackers to take keep an eye on of microphones and cameras, thus cementing Flash’s unfavorable popularity as a safety nightmare.
Changing into identified throughout social media and the higher Web as a safety danger is unhealthy for trade.
The X-Body-Choices header is an invaluable safety measure to put in force.
5. Referrer-Coverage
The aim of a Referrer-Coverage header is to permit a website online writer to keep an eye on what data is shipped when a web page customer clicks a hyperlink to talk over with any other website online.
When a web page customer clicks a hyperlink and lands on any other web page, the customer’s browser supplies details about what internet web page despatched that talk over with.
While you have a look at your server logs the referrer data is shipped that tells what websites despatched guests.
Then again, there are some eventualities the place the URL of the web page referring a customer to any other customer may just comprise delicate data which might be leaked to a 3rd social gathering.
How the Referrer-Coverage works is by means of proscribing how a lot data is shipped after a web page customer clicks a hyperlink.
A website online writer can make a selection to ship no data as to the referrer, they may be able to make a selection to ship simply the area identify or they may be able to ship all of the URL string.
There are 8 directives that may be despatched the use of the Referrer-Coverage header:
- Referrer-Coverage: no-referrer.
- Referrer-Coverage: no-referrer-when-downgrade.
- Referrer-Coverage: starting place.
- Referrer-Coverage: origin-when-cross-origin.
- Referrer-Coverage: same-origin.
- Referrer-Coverage: strict-origin.
- Referrer-Coverage: strict-origin-when-cross-origin.
- Referrer-Coverage: unsafe-url.
A not unusual referrer coverage environment is Header “no-referrer-when-downgrade” this means that that referrer data might be despatched to devoted URLs which are on HTTPS however that no referrer data might be despatched to untrusted HTTP web pages.
You will need to notice that the referrer coverage environment won't have an effect on associate hyperlinks.
The referrer data is coded throughout the touchdown web page URL, thus the referrer data and profits are recorded by means of the service provider receiving the associate referral.
How To Put in force Safety Headers
There are a couple of tactics to set safety headers, and one standard means is with an .htaccess document.
A advantage of the use of the .htaccess document is that it saves a writer from downloading any other plugin.
Poorly coded plugins can grow to be a safety possibility, so minimizing the collection of put in plugins can also be helpful.
Essential: Each and every safety header implementation goes to be other consistent with the specifics of every website online, particularly the Content material-Safety-Coverage (CSP).
WordPress Plugins For Environment Safety Headers
There are some standard plugins which are already put in on hundreds of thousands of web pages that include the choice for environment safety headers.
If you have already got those plugins put in, then the choice for the use of a plugin slightly than fussing with an .htaccess document is there for individuals who would favor the ease.
In reality Easy SSL Professional
Over 5 million web pages have already got In reality Easy SSL put in.
Upgrading to the rather priced professional model supplies the choice for putting in to 8 safety headers the straightforward means.
Redirection
The 100% loose WordPress Redirection plugin has been round for over ten years and is put in on over 2 million web pages.
This plugin lets in you to make a choice from many various preset safety headers along with the highest 5 indexed on this article.
Preset signifies that you'll make a choice from the usual directives.
In step with the Redirection WordPress obtain web page:
“ADD HTTP HEADERS
HTTP headers can also be added to redirects or all your web page that lend a hand scale back the affect of redirects or lend a hand building up safety. You'll additionally upload your personal customized headers.”
Moreover, the Redirection plugin means that you can customized craft your personal safety headers if there’s one thing there you don’t in finding.
-
Screenshot of Safety Headers UI, February 2022
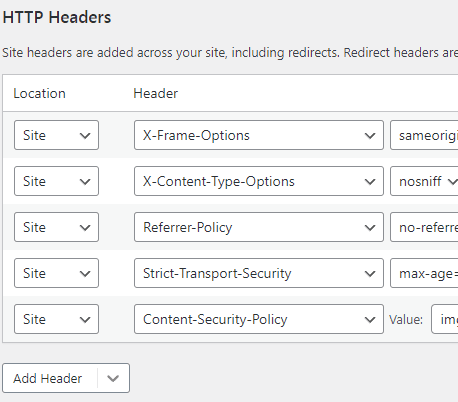
The Redirection plugin makes it simple to effectively set up the highest 5 safety headers:
- X-Body-Choices.
- X-Content material-Sort-Choices.
- Referrer-Coverage.
- Strict-Delivery-Safety.
- Content material-Safety-Coverage.
Set Safety Headers With Cloudflare
Cloudflare has a solution to set safety headers the use of their Cloudflare employees.
Cloudflare additionally has any other give a boost to web page with instructions:
“Attaching headers
To connect headers to Cloudflare Pages responses, create a _headers undeniable textual content document within the output folder of your venture.It's most often the folder that incorporates the deploy-ready HTML information and property generated by means of the construct, corresponding to favicons.
The _headers document will have to now not at all times be within the root listing of the repository. Adjustments to headers might be up to date in your website online at construct time, so remember to devote and push the document to cause a brand new construct every time you replace headers.
Header regulations are outlined in multi-line blocks.
The primary line of a block is the URL or URL trend the place the rule of thumb’s headers will have to be carried out. At the subsequent line, an indented listing of header names and header values will have to be written…”
How To Take a look at Safety Headers
Safety headers are simple to test.
SecurityHeaders.com gives a loose safety header checking carrier.
Internet auditing device Screaming Frog additionally has the choice for checking headers which is to be had within the Safety Tab.
Make Safety Headers A Phase Of Your Search engine marketing Audits
Safety headers are one thing that many publishers or Search engine marketing mavens would possibly now not imagine.
However safety headers are vital and will have to be best of thoughts in each web page audit, whether or not that audit is performed in-house or by means of third-party Search engine marketing web page auditing.
Web site safety is an Search engine marketing-related factor as a result of failure to mitigate unfavorable safety problems can opposite each ranking-related good fortune.
A unfavorable popularity can harm scores and gross sales.
Lack of seek visibility reasons devastating losses.
Enforcing safety headers is moderately simple, it will have to be a few of the best bins to test when publishing any website online.
Extra sources:
Featured Symbol: Monkey Trade Photographs/Shutterstock


Comments
Post a Comment